STEP 2–4Assess impact, risk & cost; route for approval
FINANCIAL · ENTERPRISE · MULTIFINANCE
PRIME · Enterprise Project Governance & Delivery Readiness Ecosystem
From Change Request to Digital BAST, one auditable governance flow.
Bridging business innovation & audit compliance: automating the Change Request, multi-tier approvals, testing, and digital BAST lifecycle under unified forensic auditability.
1-click demo accounts for 10 rolesMFA, RBAC & full audit trailAI behind a Privacy Gateway
7Governance gates
12Integrated modules
16AI actions + Copilot
10RBAC roles
The Governance Gap
IT projects stall in the gaps between teams, not in the code.
Scattered Approvals & Missing Trails
CRs, minutes and sign-offs bounce across emails, chats, and spreadsheets with no single source of truth or forensic audit trail.
Gate Bypass & Cutover Friction
No enforced cutover gates: critical projects go live without standardized risk checklists, rollback validation, or clear ownership.
Audit Scramble & Delayed BAST
Test evidence, go/no-go minutes, and BAST handovers must be re-collected manually whenever regulators or auditors arrive.
"Spreadsheets and operational task managers are not governance systems. They do not provide an adequate forensic audit trail when an incident or regulatory finding occurs."— Enterprise IT Governance & Risk Advisory
Competitive Differentiation
Why Conventional Task Tools Aren't Enough for Audited Enterprises
Conventional issue and task management tools are designed for team sprint velocity. PRIME is purpose-built for enterprise portfolio governance, mandatory regulatory gates, and contractual delivery accountability.
| Governance Capability | Conventional Task & Project Tools | PRIME Enterprise Ecosystem |
|---|---|---|
| Primary Focus | Team-level sprint task velocity & issue tracking | Enterprise portfolio governance & compliance lifecycle |
| Approval Gate Flow | Ad-hoc board moves without mandatory stage gates | Enforced 7-gate lifecycle; projects cannot bypass stages |
| BAST & Handover to BAU | None — requires manual external documents & email threads | Native 4-party digital BAST sign-off and hypercare workflow |
| Audit & Regulatory Readiness | Labor-intensive manual compilation during audit visits | Automated, forensic audit trail mapped to POJK & ISO standards |
| Deployment Control | Generic status labels without formal cutover sign-off | 12 readiness criteria across 5 pillars + 3-tier cutover verification |
End-to-end project lifecycle
7 gates. Every step has an owner, evidence and an audit trail.
Projects can't skip gates. PRIME ensures each stage is complete and approved before moving on.
Change Request
Business unit submission with justification & attachments.
Assessment
Impact, risk and cost estimate by the BA.
Steering Approval
Value-based tiered approval with PKI signature at Board level.
Planning
WBS, Gantt, resource allocation and schedule baseline.
Execution & SIT/UAT
Test scenarios, defects and user sign-off.
Go / No-Go
12 readiness criteria across 5 pillars and 3-tier cutover.
Release & BAST
Hypercare, then 4-party handover (BAST) to BAU.
Project lifecycle, role by role
Clear ownership at every step, from CR to BAU.
15 steps across 6 roles. Each hand-off is recorded, so everyone knows whose turn it is and auditors can see who approved what.
ROLE / GATE
GATE 1Change Request
GATE 2Assessment
GATE 3Steering
GATE 4Planning
GATE 5Build & Test
GATE 6Go / No-Go
GATE 7Release & BAST
Product Owner
STEP 1Submit CR & BRD
STEP 10Sign off UAT
STEP 15Accept handover to BAU
Business Analyst
Steering Committee
STEP 5Review & sign off (PKI at Board level)
Project Manager
STEP 6–7Create project, WBS & Gantt baseline
STEP 11Chair Go/No-Go meeting (12 criteria / 5 pillars)
STEP 14Circulate 4-party BAST
QA / Tester
STEP 8–9Run SIT, track defects, run UAT
IT Operations
STEP 12Execute 3-tier cutover
STEP 13Hypercare & stabilization
- STEP 1 · Change RequestProduct Owner — Submit CR & BRD
- STEP 2–4 · AssessmentBusiness Analyst — Assess impact, risk & cost; route for approval
- STEP 5 · SteeringSteering Committee — Review & sign off (PKI at Board level)
- STEP 6–7 · PlanningProject Manager — Create project, WBS & Gantt baseline
- STEP 8–9 · Build & TestQA / Tester — Run SIT, track defects, run UAT
- STEP 10 · Build & TestProduct Owner — Sign off UAT
- STEP 11 · Go / No-GoProject Manager — Chair Go/No-Go meeting (12 criteria)
- STEP 12 · Go / No-GoIT Operations — Execute 3-tier cutover
- STEP 13 · Release & BASTIT Operations — Hypercare & stabilization
- STEP 14 · Release & BASTProject Manager — Circulate 4-party BAST
- STEP 15 · Release & BASTProduct Owner — Accept handover to BAU
Work stepDecision gate↺ Rejected at Gate 3 returns to Assessment · No-Go at Gate 6 returns to fixes in Gate 5
Architecture & Capabilities
12 Integrated Modules Under One Governance Ecosystem
Every module seamlessly hands off state, documentation, and approvals across the 7 gates without data silos.
MODULE 01
Identity, Security & RBAC
10 role-based enterprise access controls, MFA TOTP, scrypt encryption, and granular permission matrices.
MODULE 02
Change Request Lifecycle
Standardized CR initiation, business justification, priority matrices, and change classification.
MODULE 03
Technical & Risk Assessment
Comprehensive impact scoring, architecture reviews, dependency mapping, and cost estimations.
MODULE 04
Multi-Tier Approval Engine
Configurable approval thresholds (> IDR 250M, 500M, 1B) with Board-level PKI digital signing.
MODULE 05
Project Planning & WBS
Hierarchical WBS trees, interactive Gantt charts, critical path tracking, and baseline management.
MODULE 06
Execution & Risk Governance
Milestone delivery tracking, active risk & issue (RAID) register, and resource allocation controls.
MODULE 07
SIT & UAT Testing Engine
Test scenario matrices, execution logs, defect severity triage, and business user acceptance sign-offs.
MODULE 08
Release & Go-Live Readiness
12 readiness criteria across 5 pillars, go/no-go voting, and 3-tier cutover rollback procedures.
MODULE 09
Hypercare & Stabilization
Post-implementation monitoring, SLA tracking, priority defect triage, and stability sign-off.
MODULE 10
Digital Handover & BAST
4-party digital sign-off (Business, IT Dev, IT Ops, PMO), operational documentation, and BAU transition.
MODULE 11
Document Repository & BRD
Encrypted object storage repository for BRDs, architecture diagrams, test sign-offs, and compliance evidence.
MODULE 12
Audit Trail & Forensic Logs
Immutable event logging, timestamped user actions, CSV forensic exports, and regulatory readiness reporting.
Product tour
See PRIME at work: screenshots straight from the app.
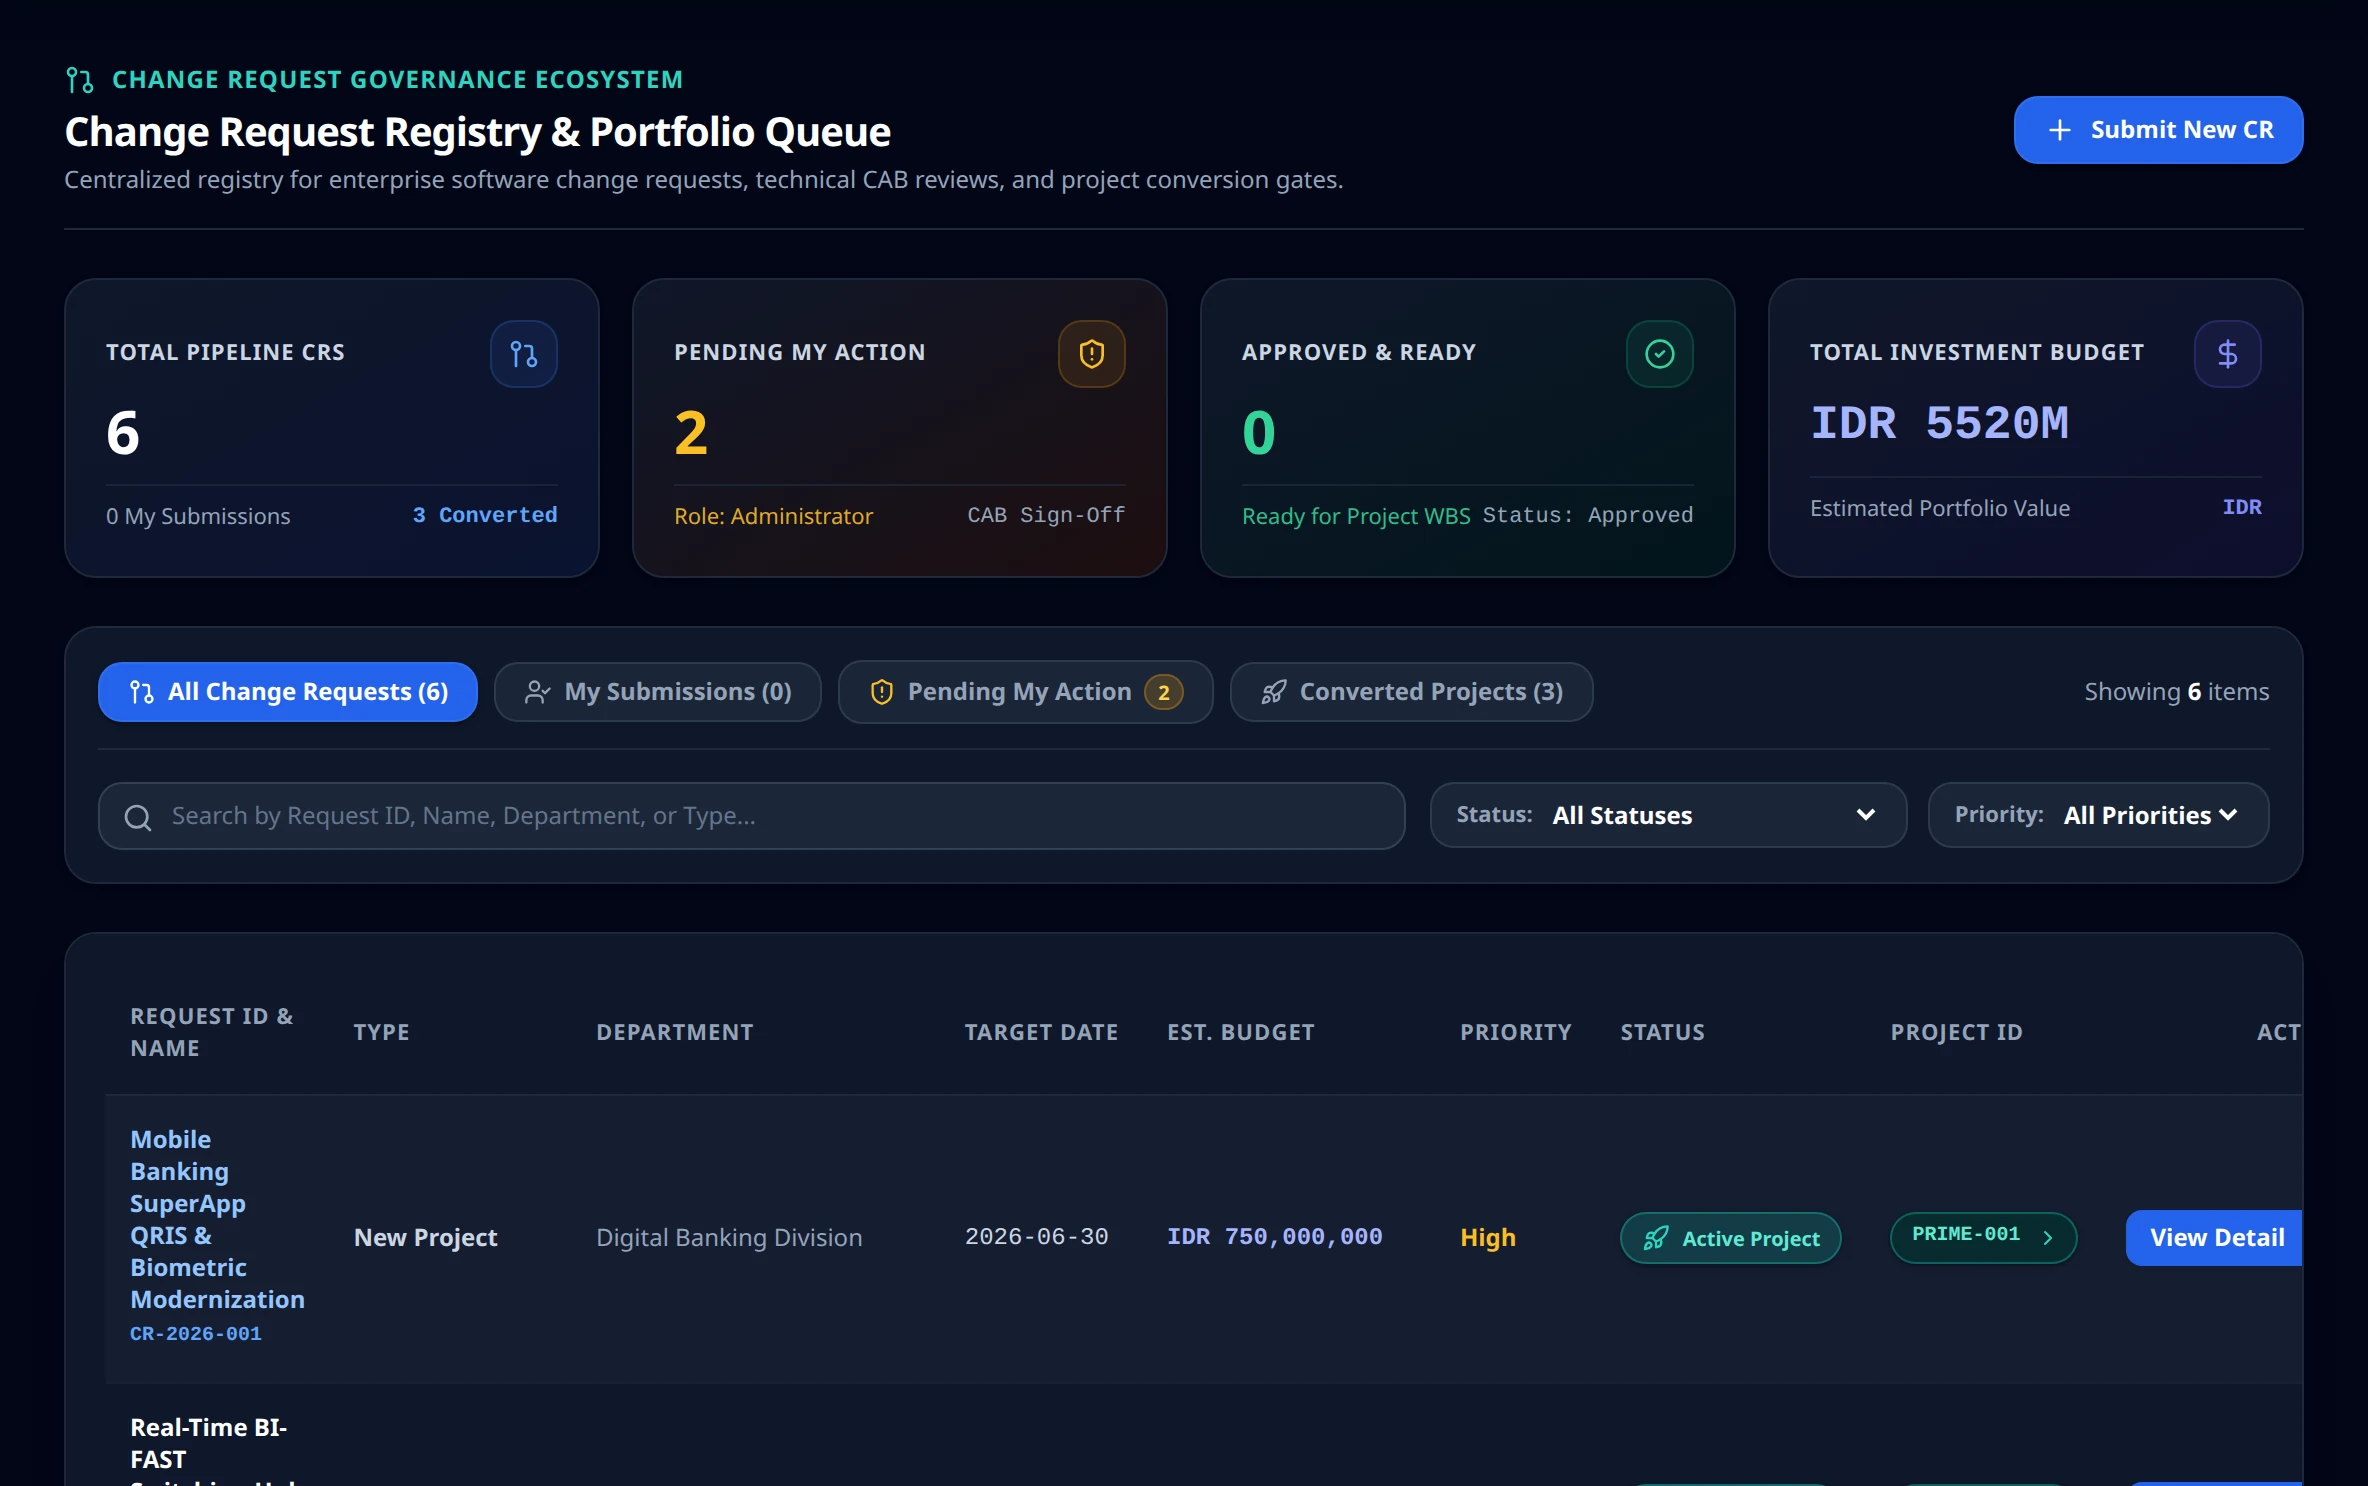
Change Requests & tiered approvals
Every request lands in the right inbox with visible SLA.
- Approval thresholds: > IDR 250M, > IDR 500M, > IDR 1B
- PKI digital signature for Board approvals
- Email notifications via Microsoft Graph
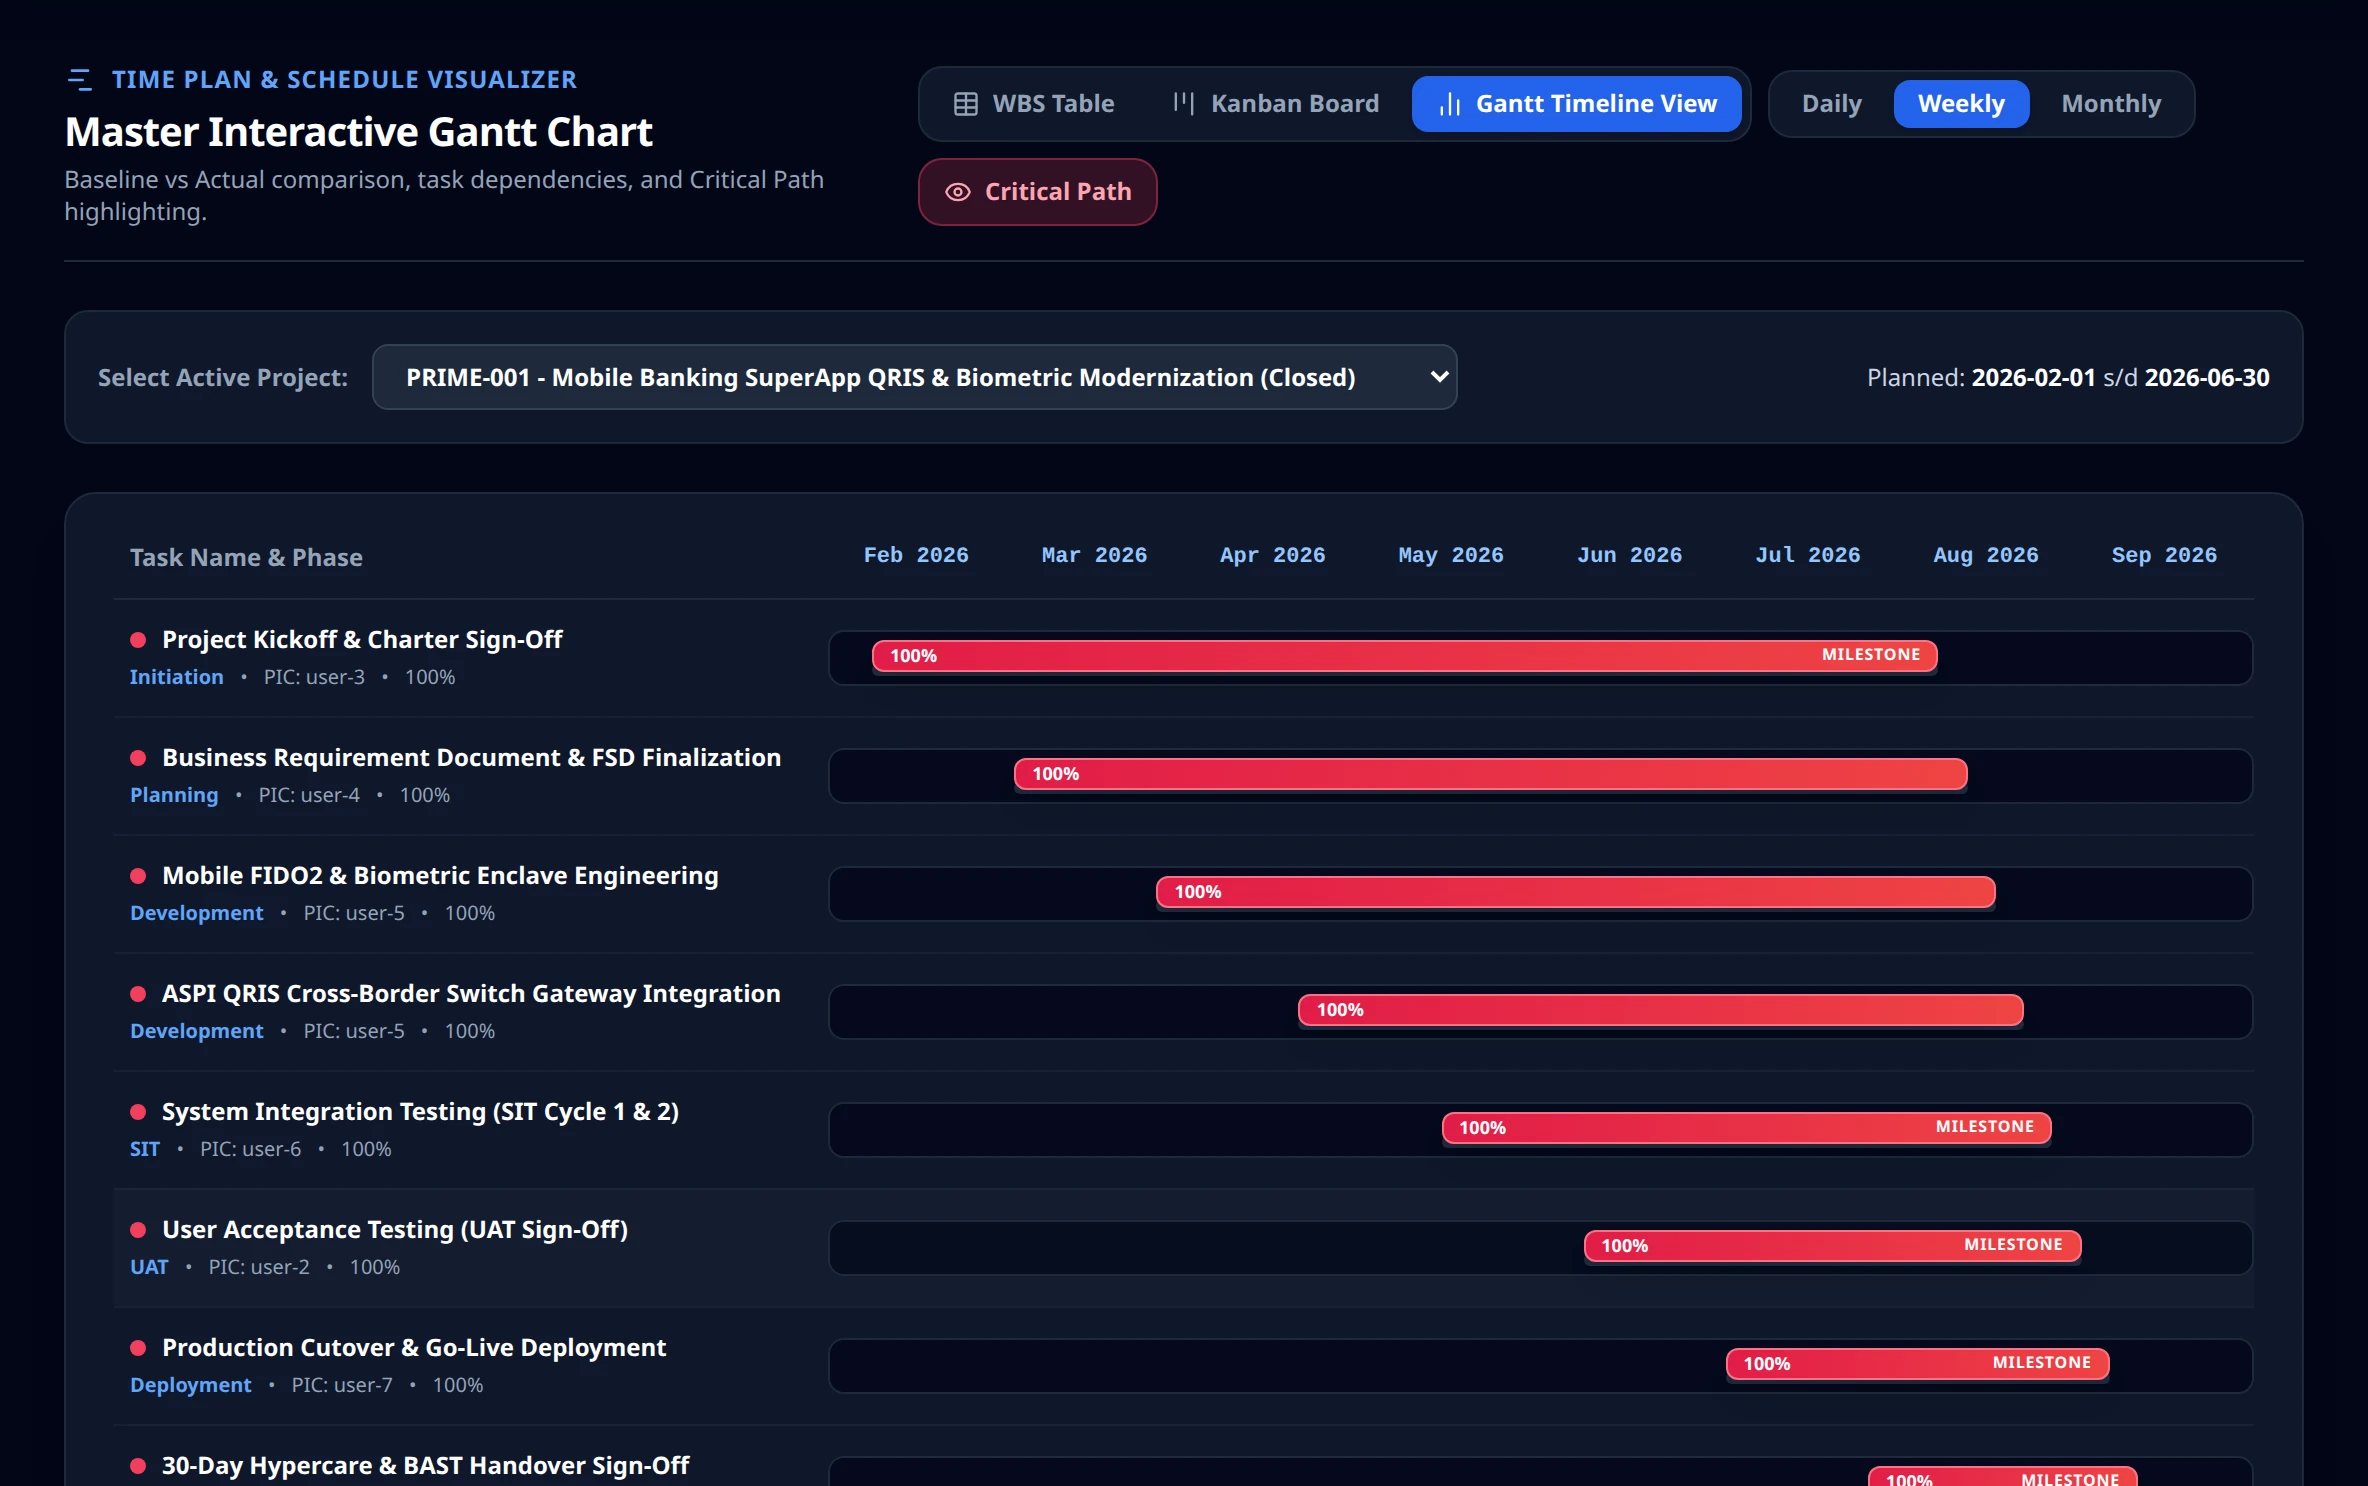
WBS & Gantt planning
Structured work plans linked directly to approved CRs.
- Multi-level WBS with weights & progress
- Interactive Gantt with dependencies
- Risk and issue register per project
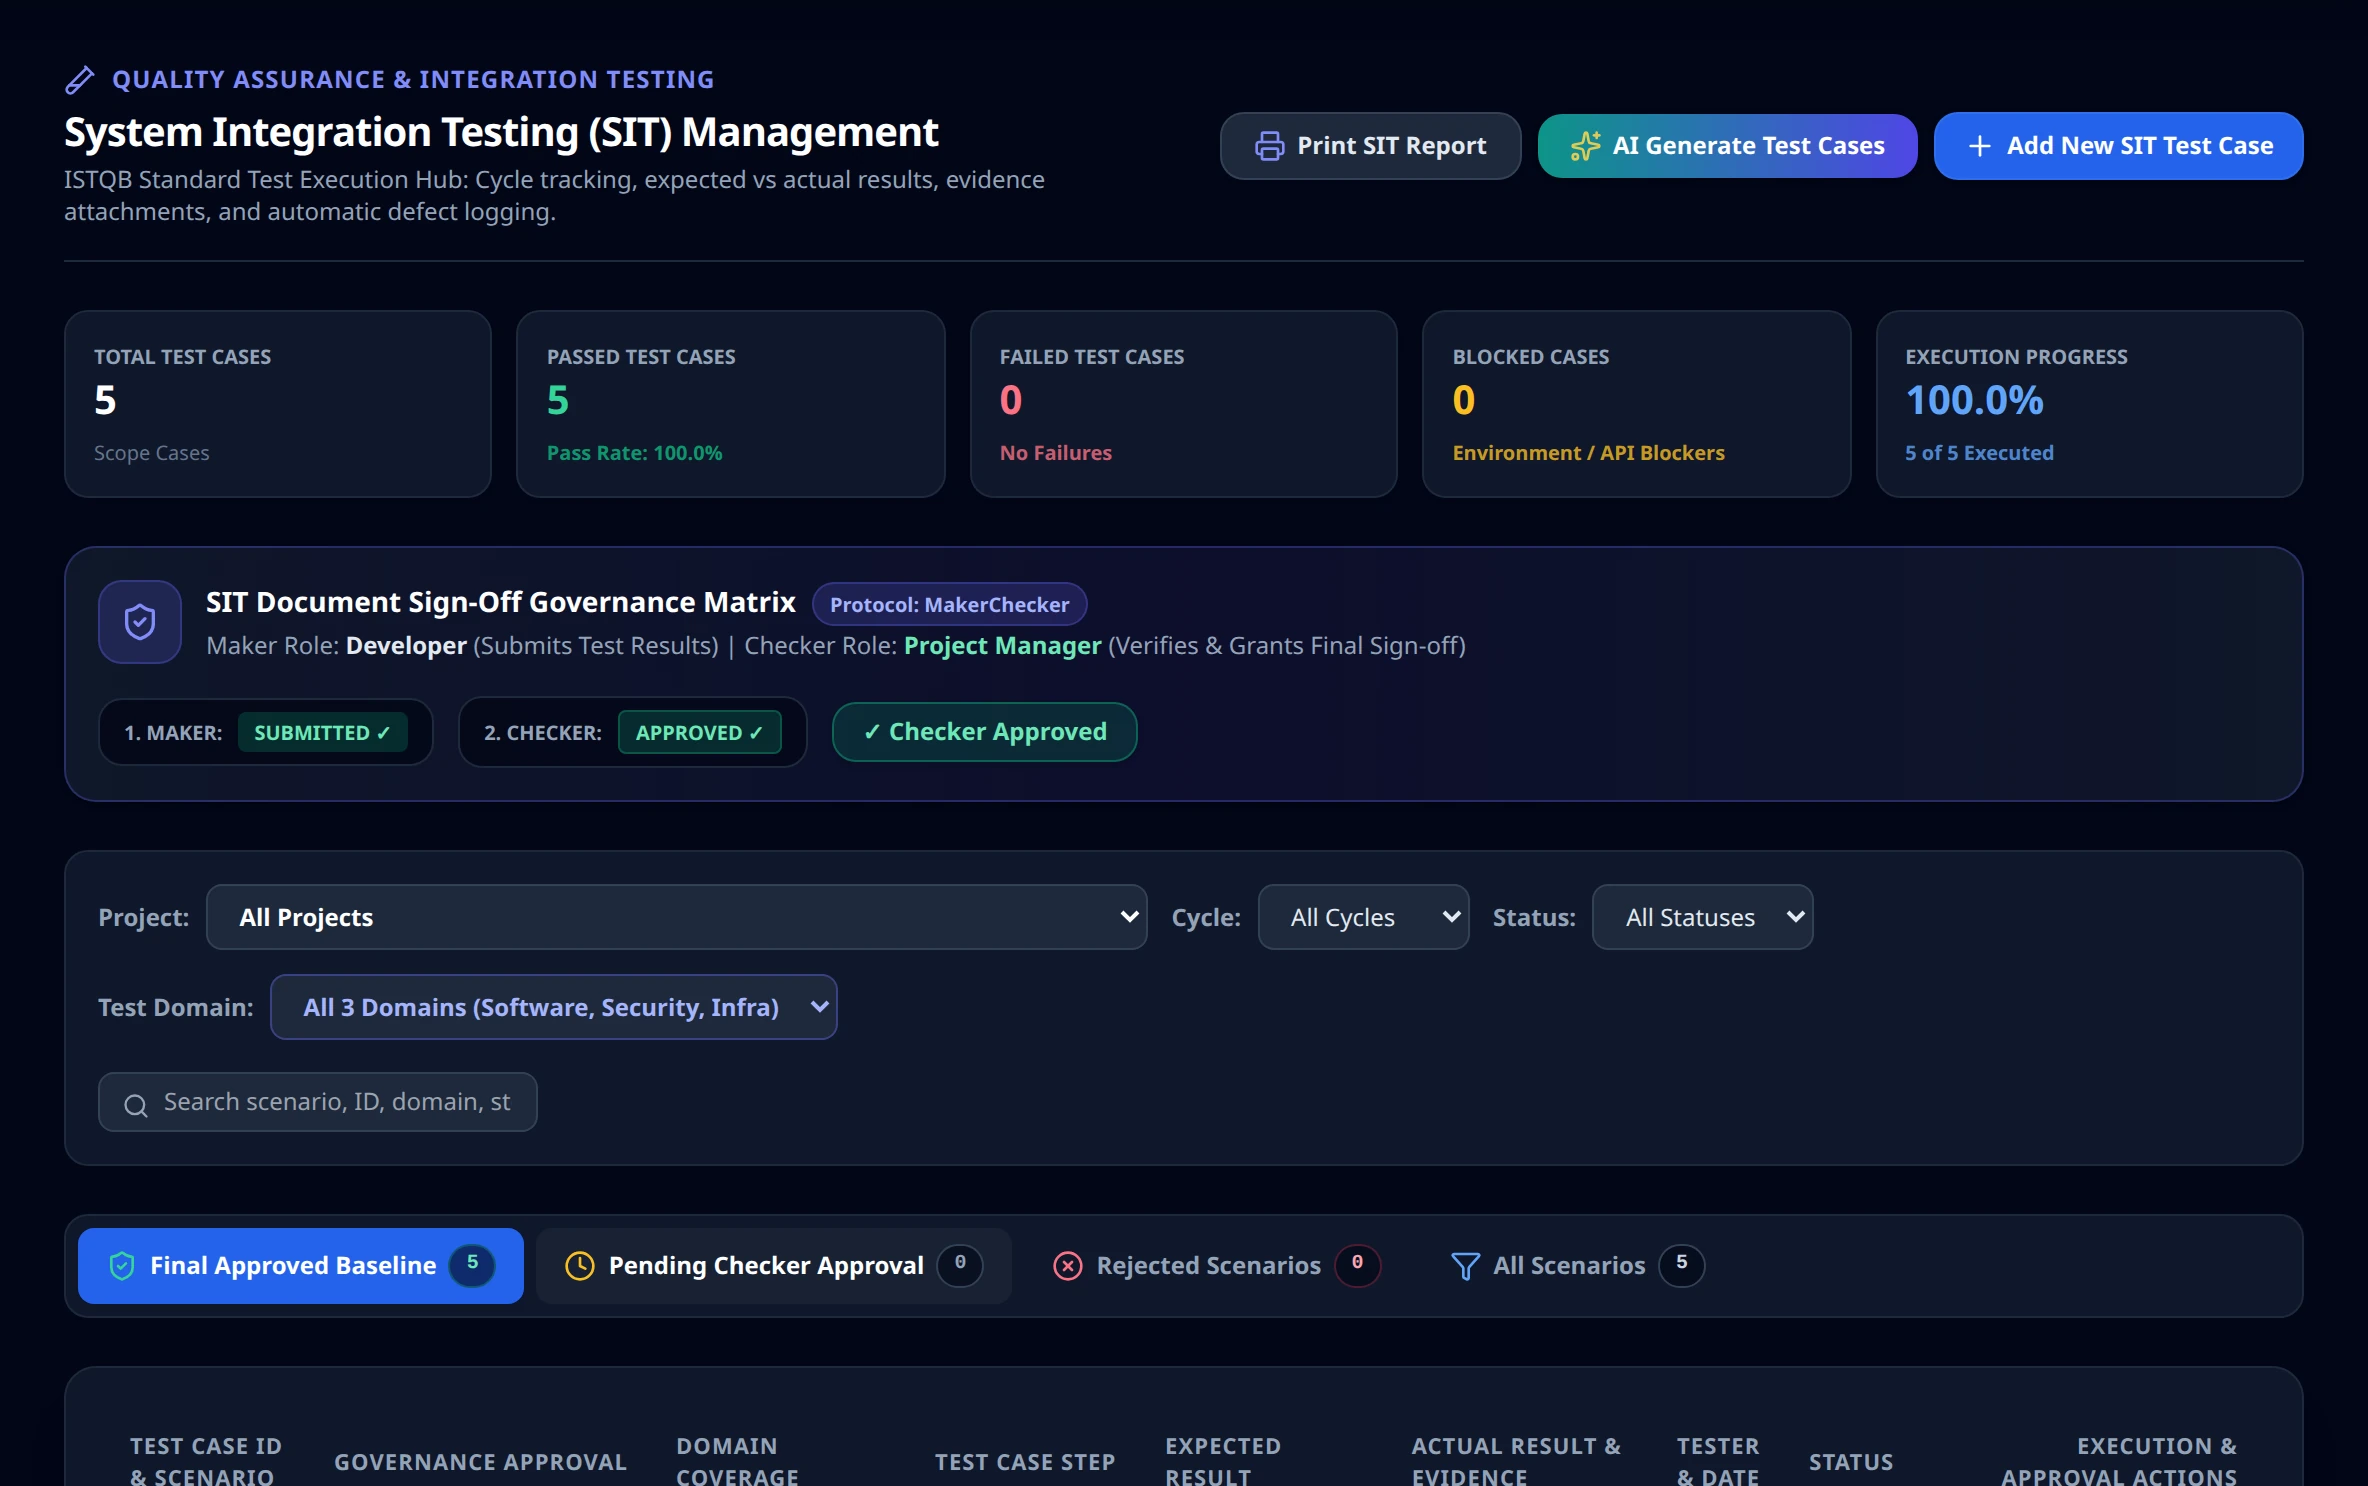
SIT & UAT testing
Test evidence stored properly instead of in personal folders.
- Test scenarios, execution and defect tracking
- UAT sign-off by business users
- Evidence attachments in object storage
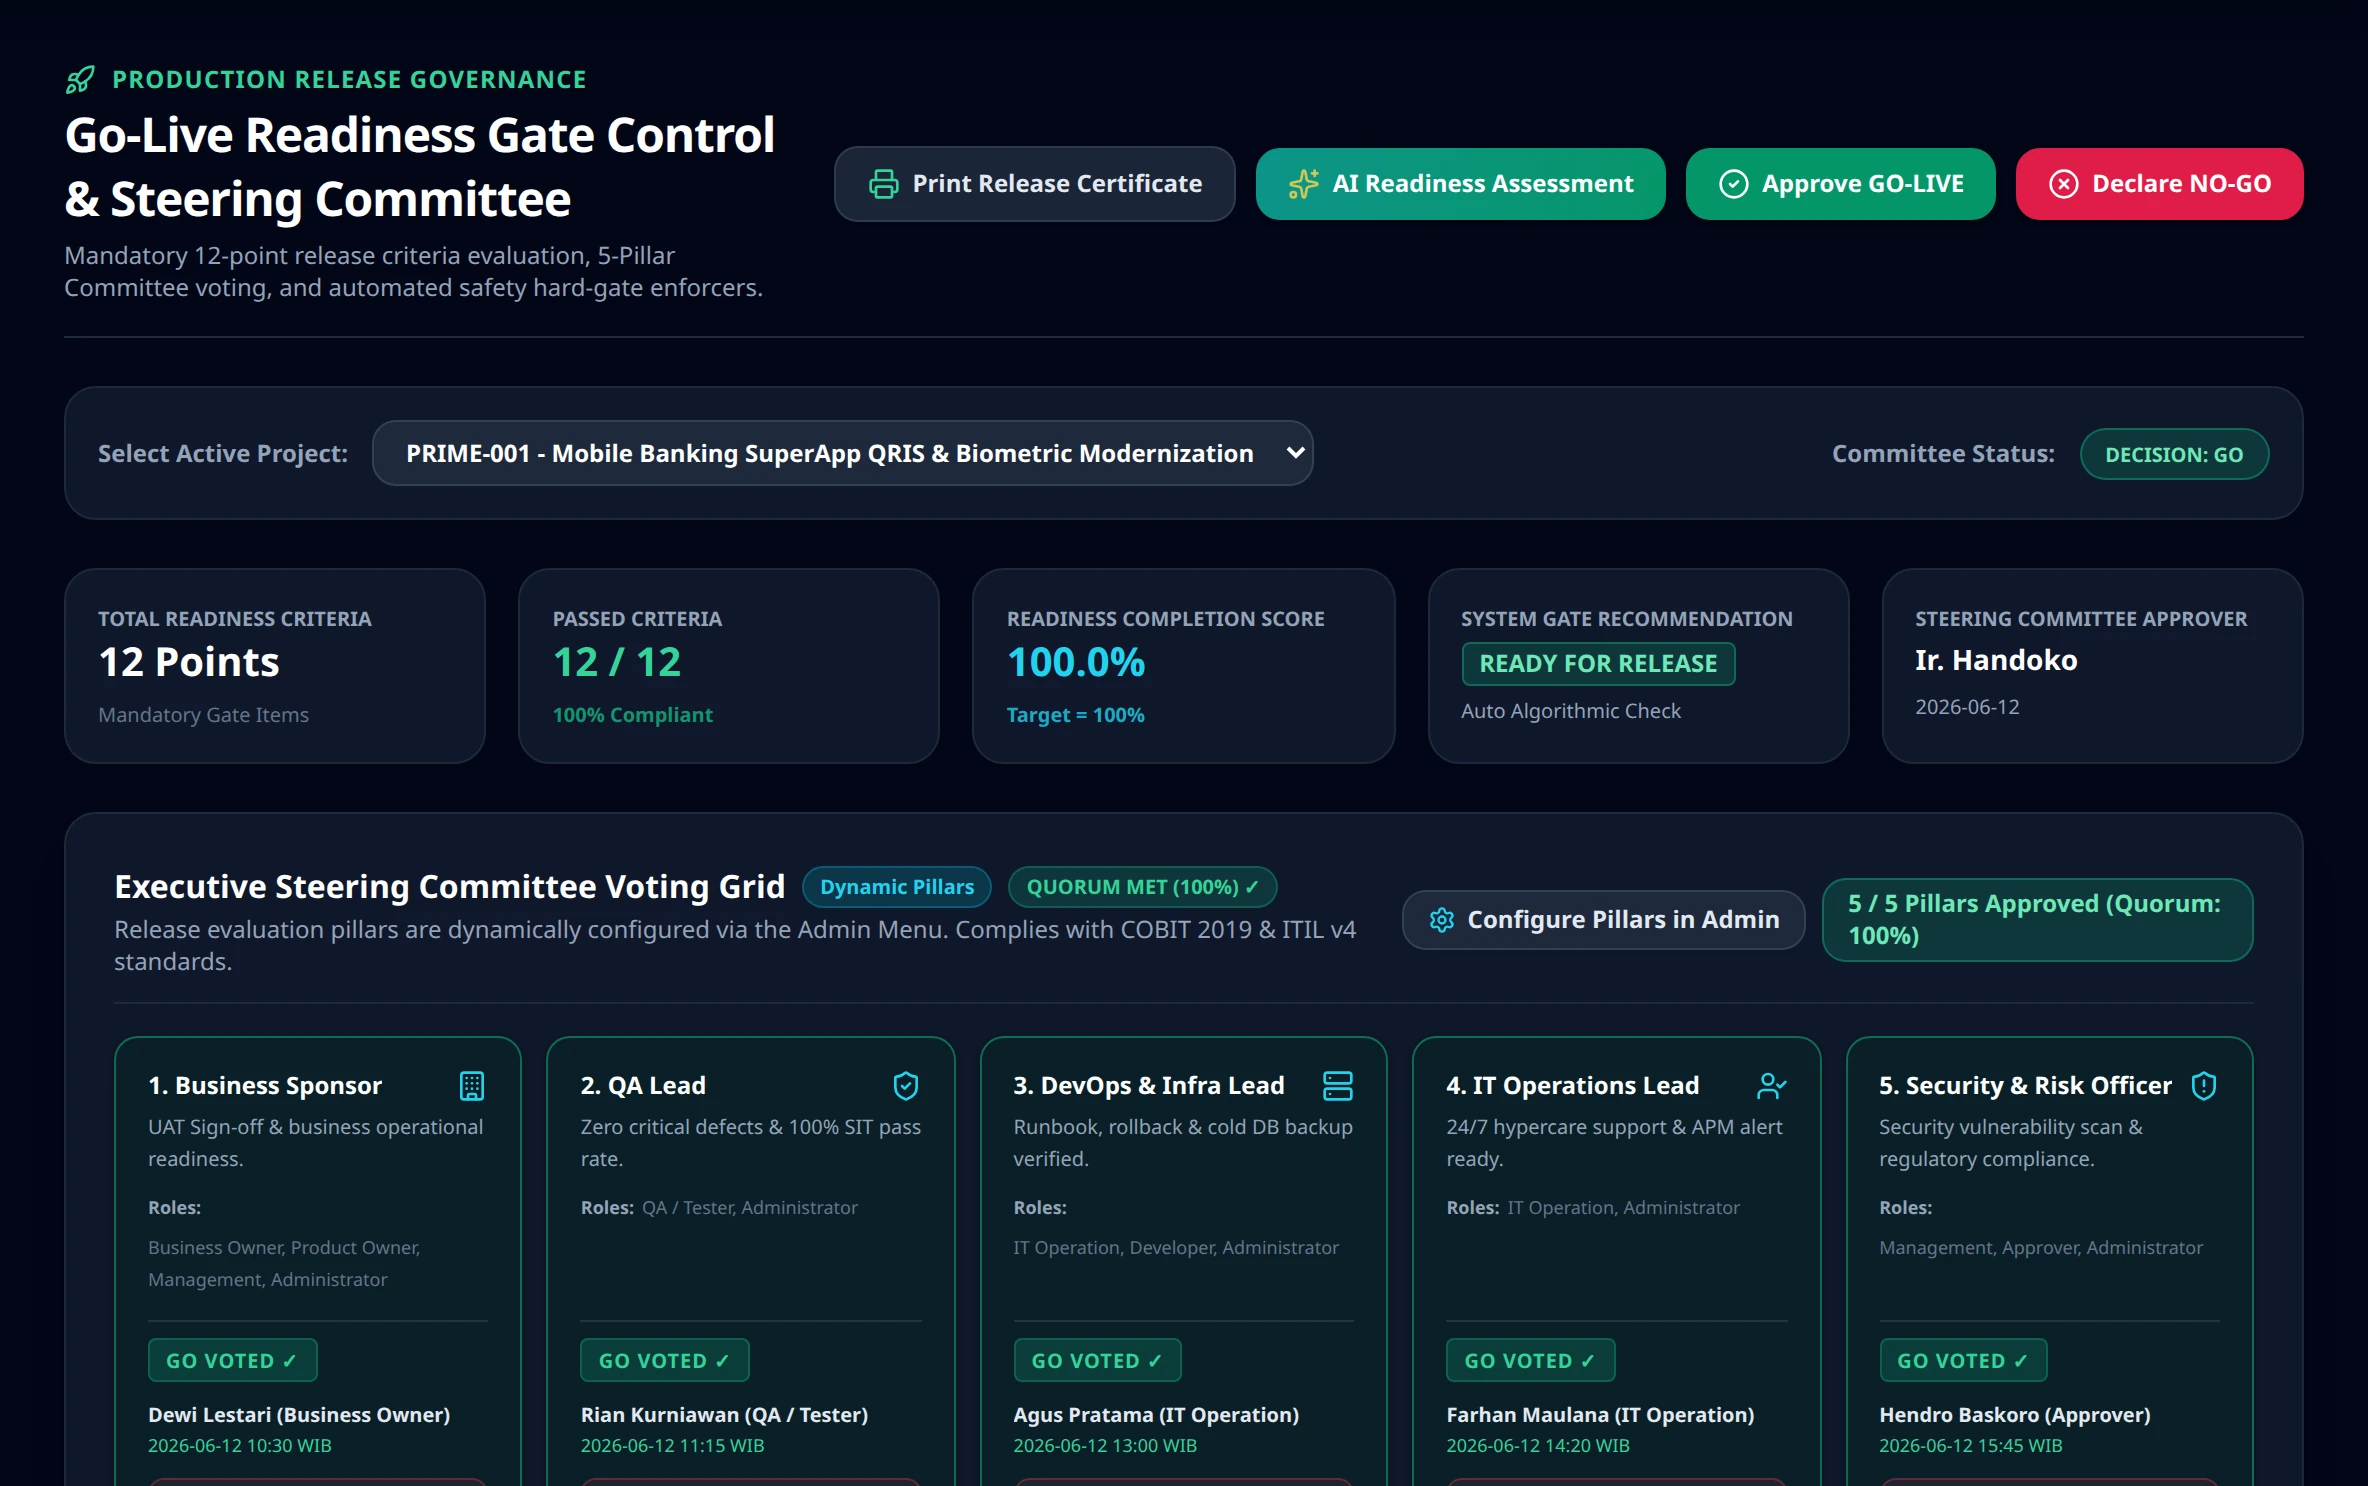
Go-Live, Hypercare & BAST
Measured release decisions and a complete handover.
- Go/No-Go checklist with 10 criteria
- 3-tier cutover and rollback plan
- 4-party handover (BAST) to operations
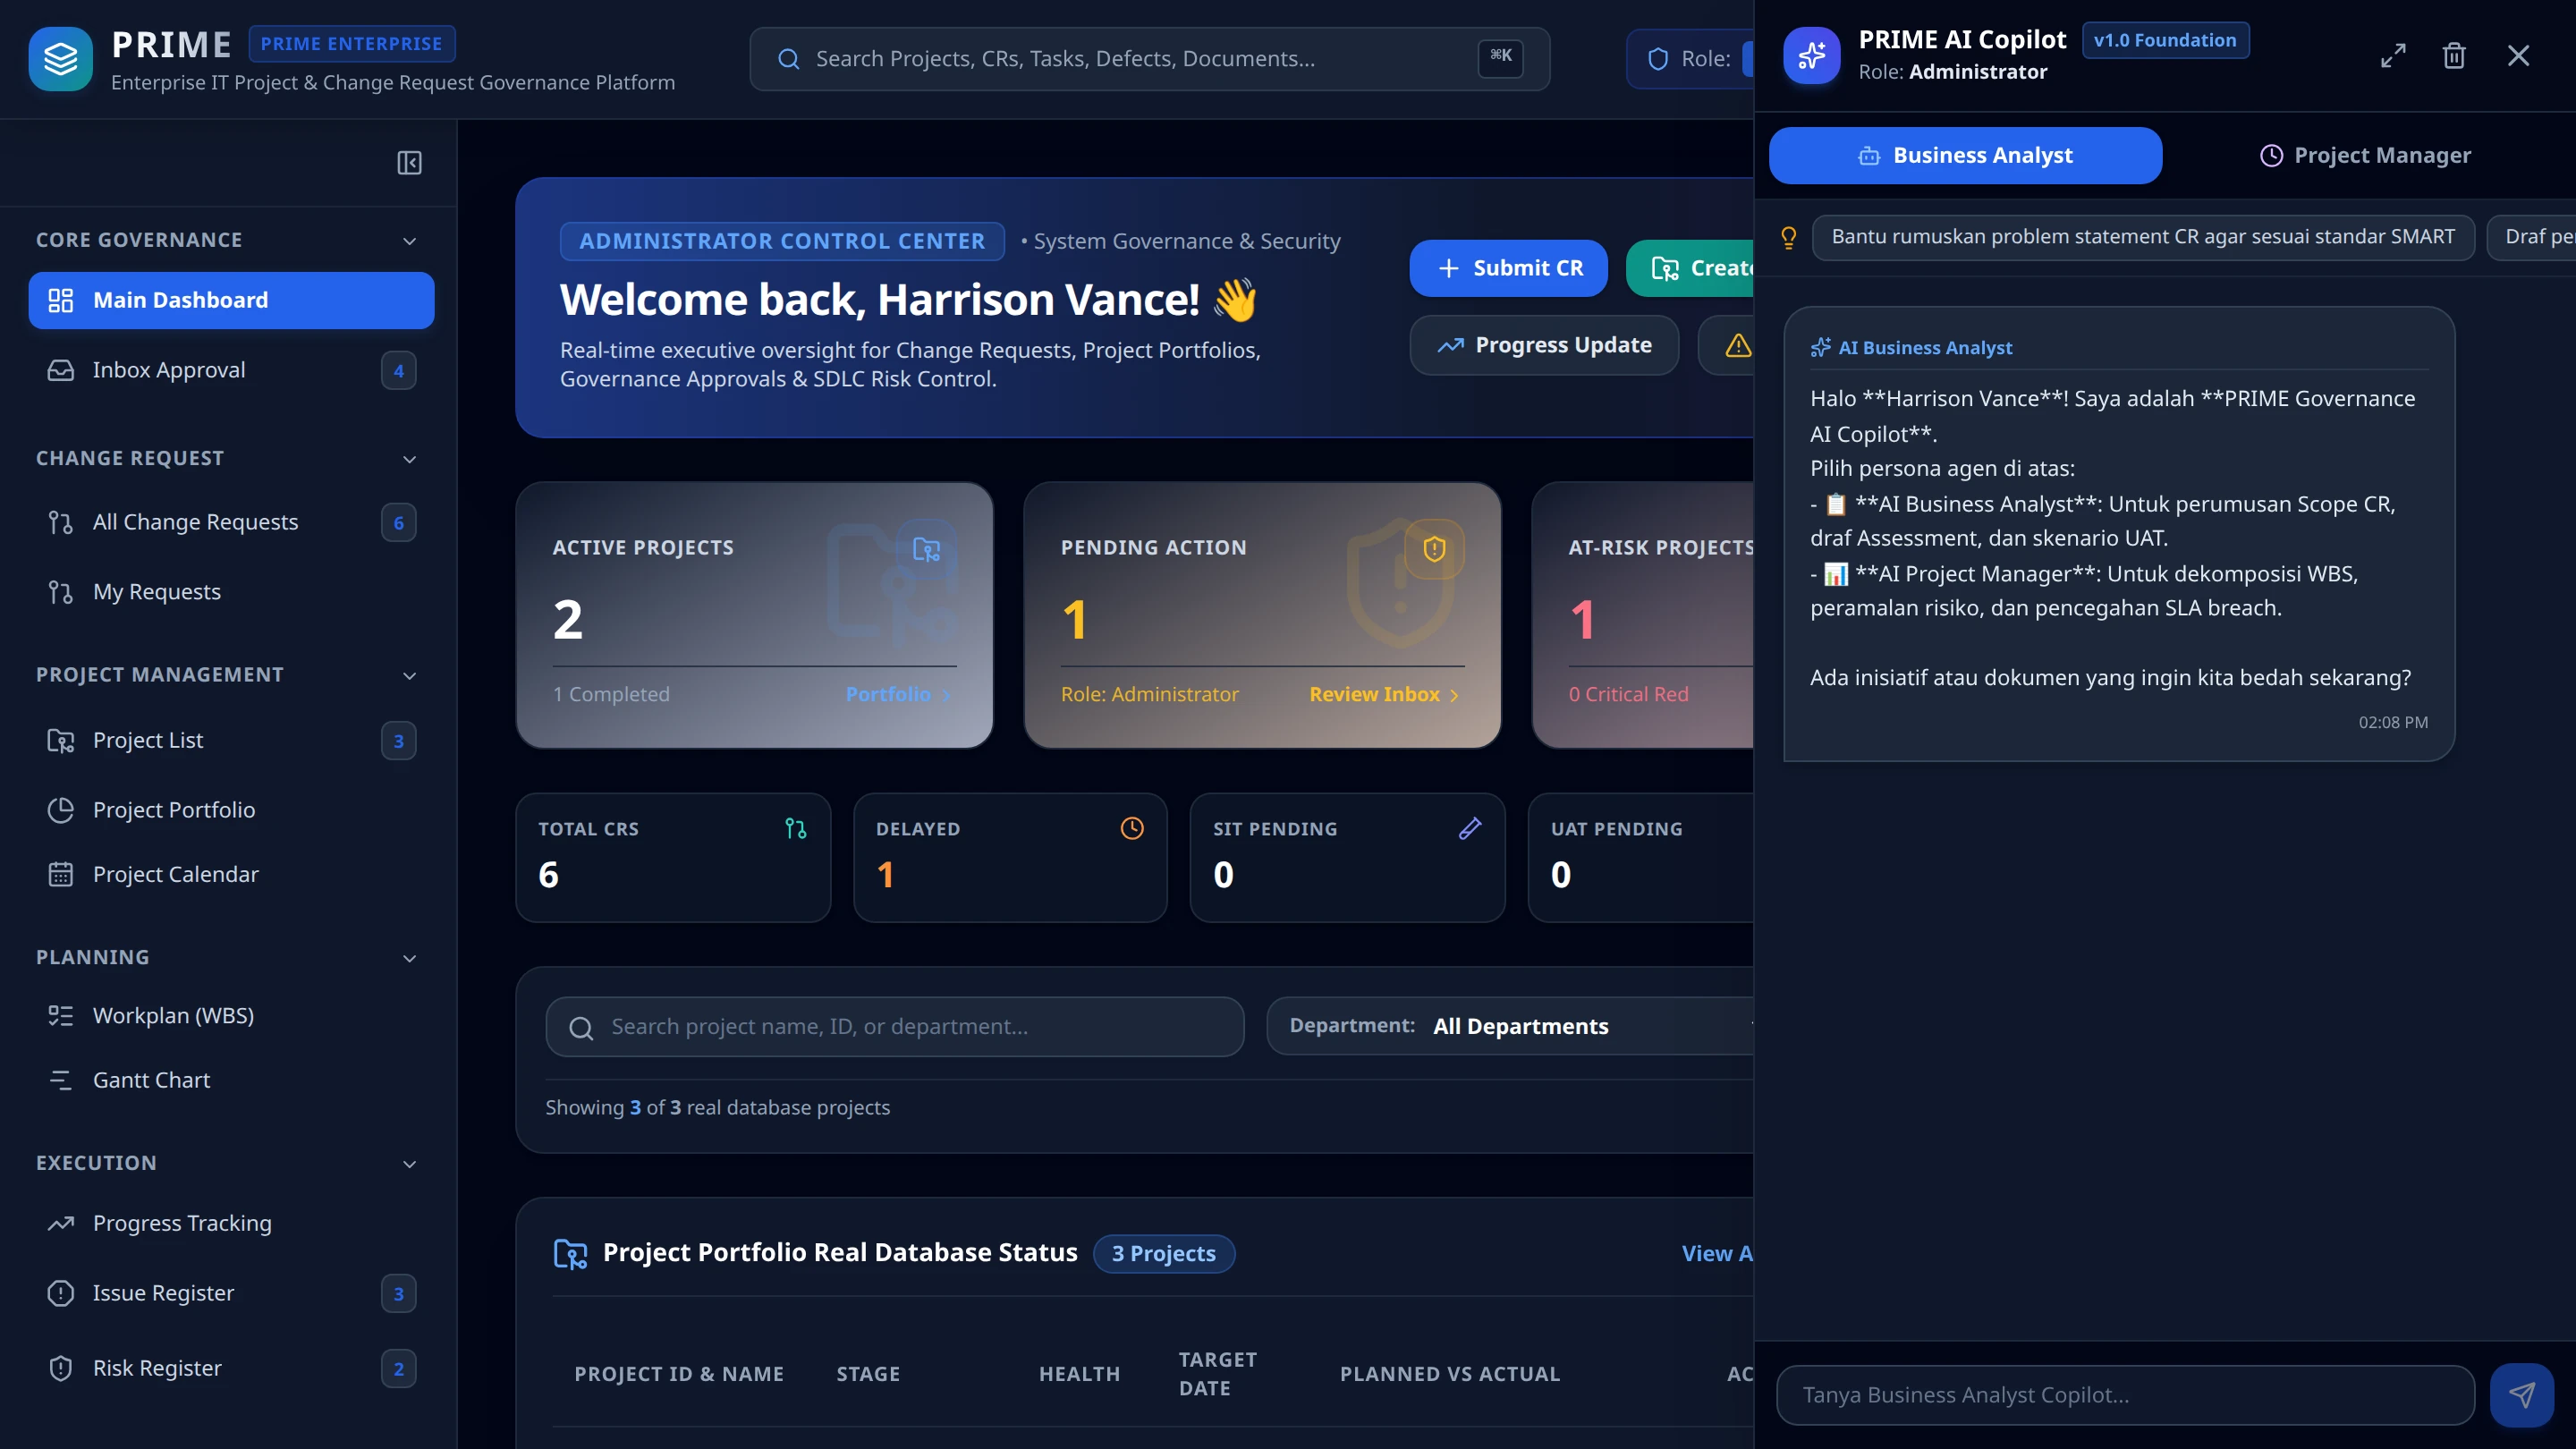
AI Copilot for BAs & PMs
16 ready-made AI actions and a Copilot chat that understands project context.
- 8 BA agent actions: BRD drafts, impact analysis, and more
- 8 PM/Governance agent actions: status summaries, risks
- Kill switch, token budget and daily quota per agent
AI Privacy Gateway
Use AI without leaking sensitive data.
Before a prompt leaves for an AI model, PRIME masks personal and secret data via a token vault, then restores it when the response comes back.
Automatic maskingNational ID, tax ID, account numbers, credit cards (Luhn), names, amounts, credentials
Custom regexAdd your organization's own data patterns
DMZ sidecarDeploy the gateway separately in a secure network zone
Local modelsRun Ollama on-premise so data never leaves your network
GeminiOpenAIClaudeAzure OpenAIOllama (local)BYOK
// original prompt
Summarize the risks of the CR owned by Budi Santoso, ID 3171xxxxxxxx0001, budget IDR 750,000,000
// what the AI model receives
Summarize the risks of the CR owned by [NAME_01], ID [NIK_01], budget [AMOUNT_01]
// response to the user: tokens restored automatically
Key risk for Budi Santoso's CR: a budget of IDR 750,000,000 requires Board approval.
Security & Regulatory Compliance
Built for Heavily Regulated Enterprises
Engineered to satisfy the stringent IT governance, risk management, and audit mandates of financial authorities.
| Regulatory Standard | Compliance Focus Area | PRIME Platform Implementation |
|---|---|---|
| POJK MRTIFinancial Services Authority | IT Risk Management, Change Management & Segregation of Duties | Strict RBAC separation across 10 roles, mandatory multi-tier approvals before cutover, complete forensic audit logs. |
| ISO/IEC 27001:2022Global InfoSec Standard | Control A.8.25 (Secure Development) & A.8.24 (Cryptography) | MFA TOTP enforcement, AES-256-GCM encryption for credentials, scrypt password hashing, encrypted artifact storage. |
| COBIT 2019ISACA Governance Framework | BAI06 (Managed IT Changes) & BAI07 (Acceptance & Transition) | 7-gate automated transition, 12 Go-Live readiness criteria across 5 pillars, formal 4-party BAST handover. |
| ISO 9001 / ITIL v4Quality & Service Management | Quality Assurance & Service Transition into BAU Operations | Dedicated SIT/UAT validation gates, post-cutover Hypercare stabilization period, SLA-driven defect management. |
MFA TOTPTwo-factor auth with 5 recovery codes
AES-256-GCMEncryption for secrets & credentials
RBAC10 roles and 28 granular permissions
Audit TrailEvery action logged, CSV forensic export
Privacy GatewayZero data leaks to external AI models
On-Premise ReadyDeploy in air-gapped DMZ or private VPC
Role SeparationEnforced segregation of duties across teams
scrypt HashingBrute-force resistant password security
Note: ISO 27001, COBIT 2019 and POJK MRTI references describe internal platform architectural controls mapped to these frameworks.
Enterprise Adoption
30-Day Low-Risk Pilot Program
Experience PRIME with your real-world Change Requests and workflows in an isolated, production-grade sandbox.
WEEK 1
Setup & Configuration
Sandbox provisioning, role mapping (10 roles), approval thresholds, and custom workflow alignment.
WEEKS 2–3
Live Lifecycle Execution
Run 2–3 real Change Requests through CR assessment, WBS planning, SIT/UAT evidence logging, and Go-Live gate.
WEEK 4
Audit Review & Evaluation
Evaluate audit trail generation, executive dashboard reporting, digital BAST sign-off, and organizational ROI.
Ready to eliminate governance gaps in your organization?
Schedule an executive presentation or launch your 30-day sandbox pilot with our dedicated implementation team.
Enterprise Delivery Readiness
See PRIME's 7-gate governance flow for yourself.
Test drive our 1-click role accounts in the live demo sandbox, or book a private executive presentation for your governance team.